
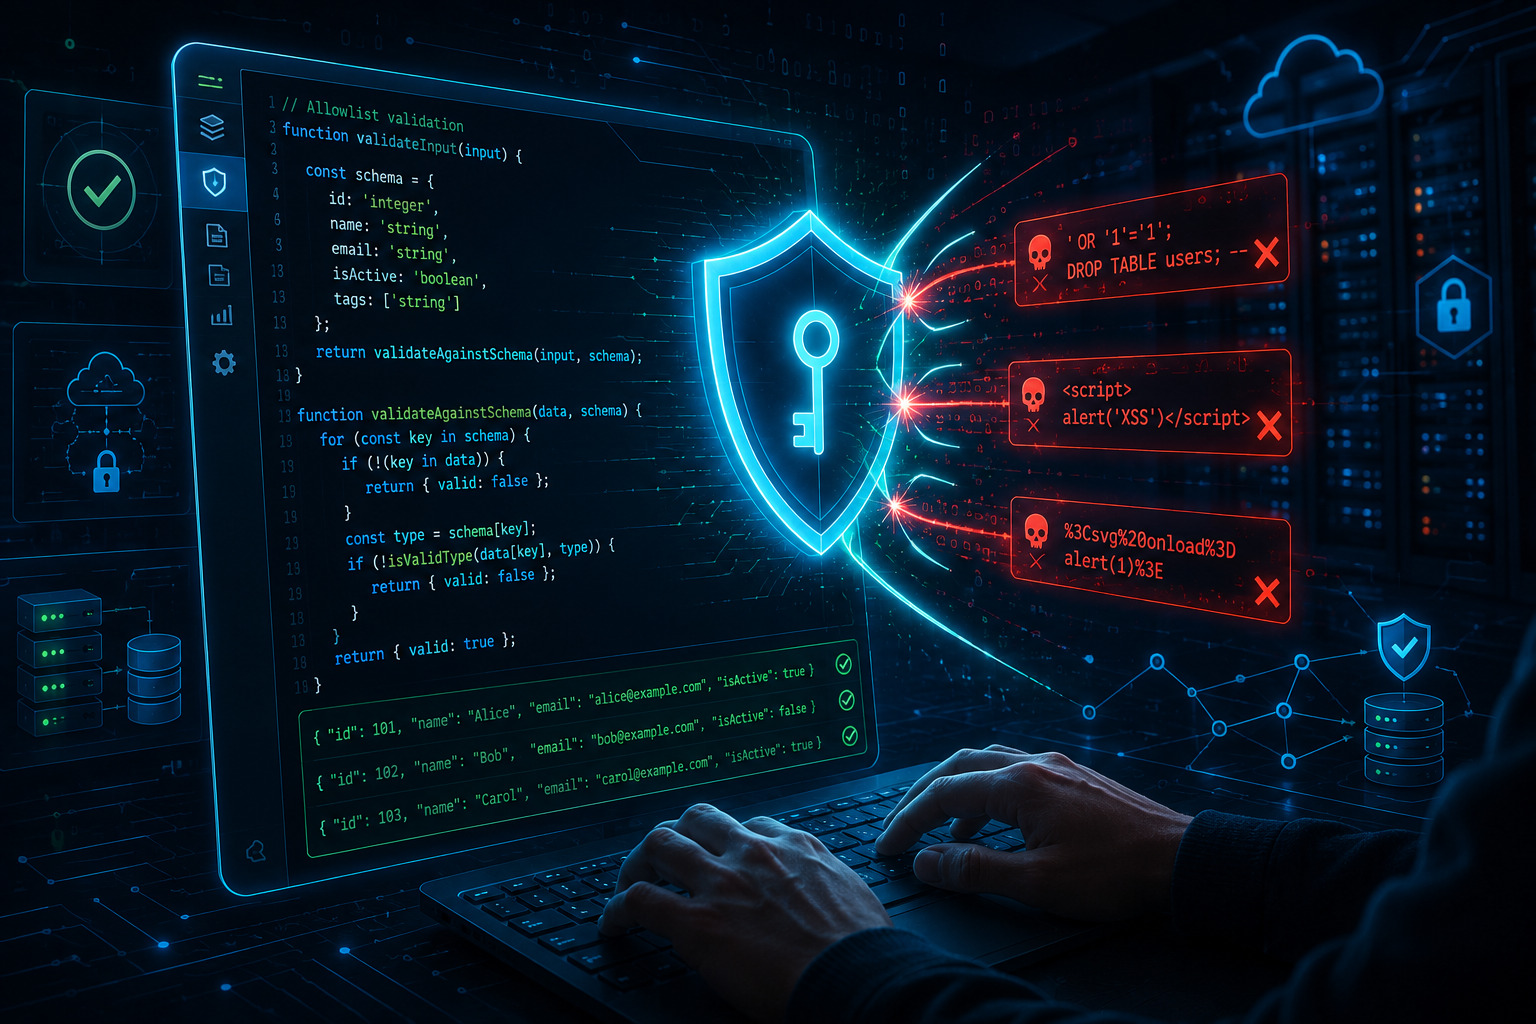

Mastering the process of implementing allowlist validation effectively code safeguards enterprise software against advanced injection attacks and unauthorized data manipulation. At Secure Coding Practices, expert security engineers emphasize that reactive blocklists leave backend systems inherently vulnerable to novel bypass techniques and multi-layer encoding exploits across production.
Transitioning away from outdated filtering toward proactive permit-based frameworks guarantees absolute boundary control and prevents critical application vulnerabilities across all modern environments.
By defining strict structural schemas and expected data formats rather than chasing infinite malicious patterns, development teams eliminate dangerous parsing ambiguities and ensure robust enterprise application integrity right now.
Core Takeaways for Implementing Allowlist Validation Effectively Code
Implementing allowlist validation effectively code provides crucial foundational advantages for modern enterprise security architectures.
- Proactive permit-based verification eliminates zero-day vulnerability risks by strictly accepting only pre-approved schemas.
- Transitioning away from reactive blocklists drastically reduces long-term maintenance overhead and constant patch cycles.
- Enforcing rigid server-side data checks across all endpoints prevents sophisticated encoding and injection bypass attempts.
Why Does Implementing Allowlist Validation Effectively Code Protect APIs?
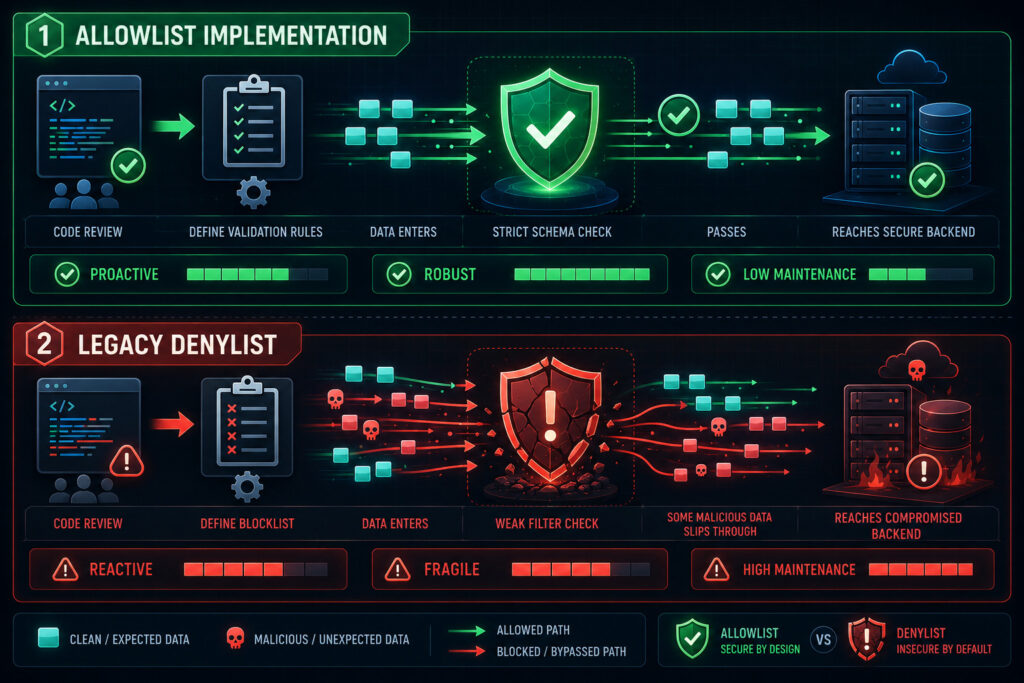
When modern web applications handle complex data exchanges, implementing allowlist validation effectively code ensures that all incoming parameters match exact business expectations. Unlike legacy filtering methods that attempt to guess every potential malicious string, a positive verification model guarantees that unauthorized structures are rejected at the application gateway before reaching internal databases.
Furthermore, developers focusing on implementing allowlist validation effectively code eliminate vulnerabilities stemming from type juggling, truncation errors, and unexpected payload formats. By enforcing strict data types, maximum length boundaries, and canonical character sets, engineering teams close off traditional attack paths that threat actors exploit through parameter tampering.
This proactive architectural posture fundamentally transforms how software handles untrusted data streams.
How Does Implementing Allowlist Validation Effectively Code Compare to Legacy Filters?
Allowlist validation provides stronger input control than legacy filters because it accepts only values that match predefined rules. Traditional denylist filters rely on identifying known threats, which leaves room for unexpected inputs to bypass restrictions. Understanding the differences in allowlist vs denylist validation shows why checking inputs against approved criteria is a more reliable approach for applications running at scale.
| Validation Architecture | Core Operational Principle | Security Effectiveness | Maintenance Burden |
| Denylist (Restriction) | Blocks known malicious patterns | Reactive and Fragile | Extremely High |
| Allowlist (Permit) | Permits pre-approved schemas | Proactive and Robust | Low and Stable |
By moving away from endless patch cycles, implementing allowlist validation effectively code ensures long-term architectural stability and a predictable security posture across all backend microservices.
Why Do Industry Standards Require Implementing Allowlist Validation Effectively Code?
Credits: OWASP LAGOS CHAPTER
Leading software security frameworks mandate strict structural checks to ensure that executing tasks related to implementing allowlist validation effectively code remains a core pillar of enterprise defense. When building resilient backend services, assuming data safety based on client-side controls introduces severe architectural vulnerabilities.
Official software development guidelines emphasize the critical need for rigorous perimeter verification before any data enters core application layers:
“Applications should treat all external input as untrusted and enforce rigorous type, length, and format validation before processing.” – Microsoft Secure Coding Guidelines
Adopting these official architectural guidelines ensures that enterprise software remains protected against injection flaws and unexpected parsing exploits.
How Can Engineering Teams Streamline Implementing Allowlist Validation Effectively Code?
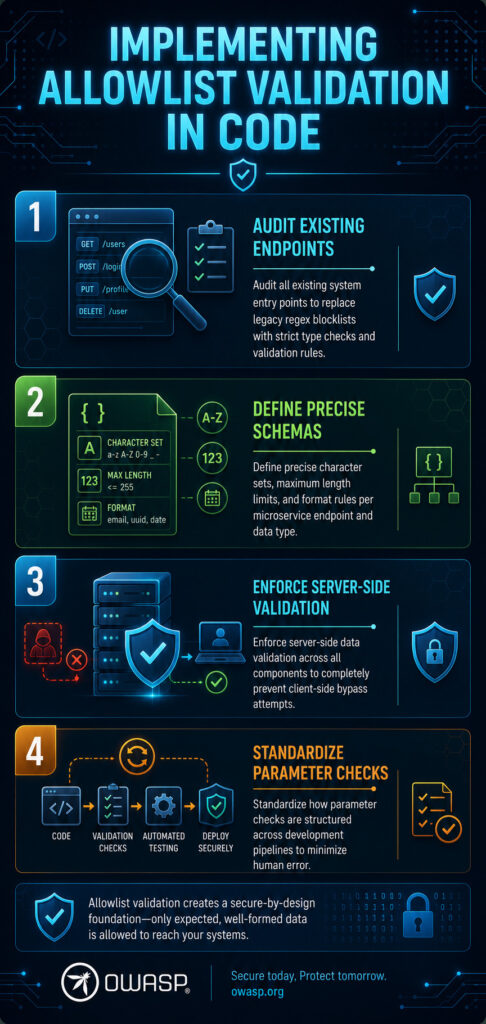
Engineering teams can adopt allowlist validation more efficiently by defining accepted input formats, applying consistent validation rules, and testing them across application components. A structured approach helps developers maintain consistent security checks without adding unnecessary complexity. The input validation allowlist approach explained shows how these practices can help protect backend microservices from unexpected or malicious inputs.
By standardizing how parameter checks are structured across development pipelines, teams can minimize human error and ensure that every service enforces rigorous boundary policies consistently.
- Audit all existing system entry points to replace legacy regex blocklists with strict type checks.
- Define precise character sets, maximum length limits, and format rules per microservice endpoint.
- Enforce server-side data validation across all components to completely prevent client-side bypass attempts.
How Do Federal Security Standards Shape Implementing Allowlist Validation Effectively Code?
Government cybersecurity agencies and federal standards bodies heavily emphasize that implementing allowlist validation effectively code is paramount for stopping injection attacks. Relying on incomplete filter lists leaves systems open to sophisticated exploitation across enterprise networks.
Federal architecture frameworks require explicit boundary enforcement to protect backend services from malicious manipulation:
“Systems must validate all untrusted inputs against an authoritative specification before processing, utilizing positive allowlisting strategies rather than fragile denylists.” – CISA Secure by Design Guidance
Adhering to these rigorous benchmarks ensures that enterprise software remains resilient against evolving attack vectors.
Why Do Enforced Schemas Block Injections?
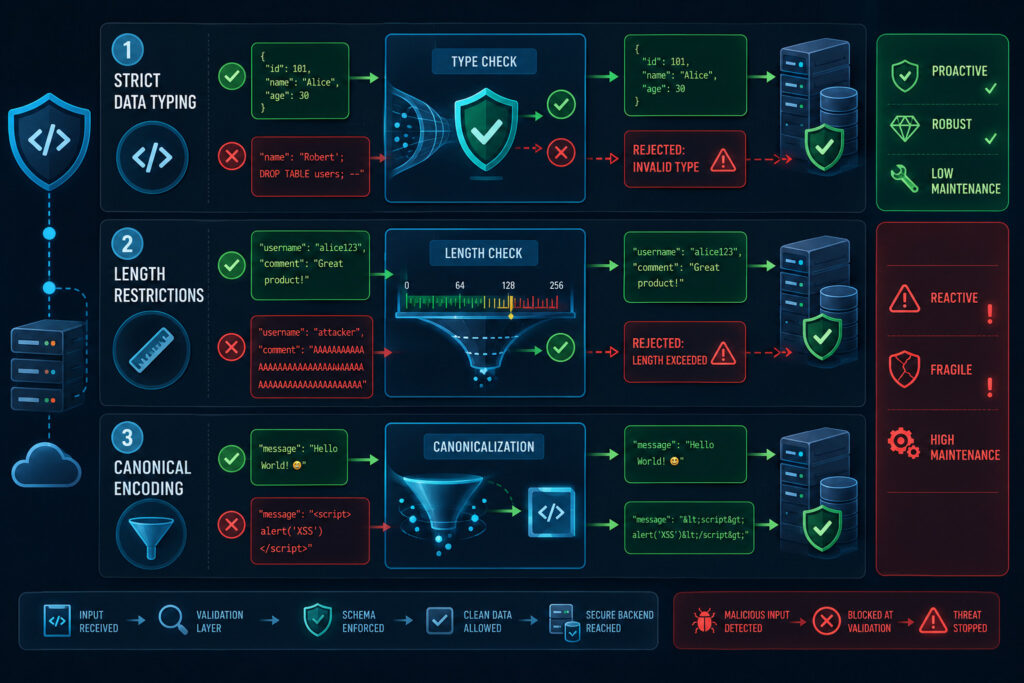
Implementing allowlist validation effectively code ensures that advanced security mechanisms stop malicious payloads before they ever reach core database logic. By enforcing strict schema rules, modern applications maintain a resilient security posture across every entry point.
Furthermore, this proactive filtering layer stops malicious actors from exploiting parsing quirks, type juggling, or unexpected data formats during runtime execution.
- Strict data typing ensures malicious SQL or command strings are dropped immediately at the application edge.
- Pre-defined length restrictions prevent buffer overflow attempts and unexpected memory exhaustion.
- Canonical character enforcement neutralizes cross-site scripting (XSS) payload delivery attempts.
Why Avoid Legacy Denylists?
Legacy denylists can leave applications vulnerable because they only block known malicious inputs. Attackers may bypass these filters through unexpected characters, encoding techniques, or new attack patterns. As explained in input validation denylist approach risks, relying on reactive filtering can leave gaps in application security. Allowlist validation offers a more reliable approach by accepting only inputs that match predefined rules.
Transitioning away from outdated filtering methods ensures that software remains robust against emerging cyber threats by enforcing rigid data boundaries across every endpoint.
- Relying on reactive blocklists exposes core databases to SQL injection and remote code execution vulnerabilities.
- Failing to anticipate creative evasion tactics leaves applications completely unprotected against zero-day payloads.
- Constant maintenance overhead diverts valuable engineering hours away from building robust, proactive software defenses.
FAQ
Why choose allowlisting over denylisting?
Allowlisting enforces a strict security posture by permitting only verified, expected data formats, eliminating the risk of novel bypasses inherent in reactive blocklists.
How do legacy denylists fail?
Attackers easily bypass blocklists using obfuscation, alternative encodings, or zero-day variations that signature-based filters miss entirely.
What makes permit models maintainable?
Positive validation rules rely on static business logic boundaries, reducing the constant patch cycles required by reactive filters.
Can sanitization replace allowlists?
Basic sanitization often strips characters inconsistently, leaving complex parsing ambiguities that malicious actors can exploit.
How to transition to allowlists?
Engineering teams can map expected data structures endpoint by endpoint, replacing regex block rules with strict type checking and canonical character normalization.
Securing Enterprise Systems Through Proactive Verification
Embracing proactive verification architectures is essential for ensuring enduring software resilience against evolving cyber threats. Relying on outdated reactive blocklists leaves production systems vulnerable to creative encoding bypasses and severe injection attacks.
Engineering teams must systematically transition toward strict permit models that enforce absolute boundary controls across every system layer. Mastering the workflow of implementing allowlist validation effectively code guarantees absolute data integrity and safeguards enterprise networks from emerging risks.
Ready to elevate your software security standards and master advanced enterprise defense techniques? Join the Secure Coding Practices Bootcamp to build completely secure enterprise architectures and protect critical systems today.
References
- https://learn.microsoft.com/en-us/dotnet/standard/security/
- https://www.cisa.gov/resources-tools/resources/secure-by-design