Skip to content
No results
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Input Validation & Sanitization

Benefits Parameterized Queries Security Performance for Web Apps

Benefits Parameterized Queries Security Performance for Web Apps

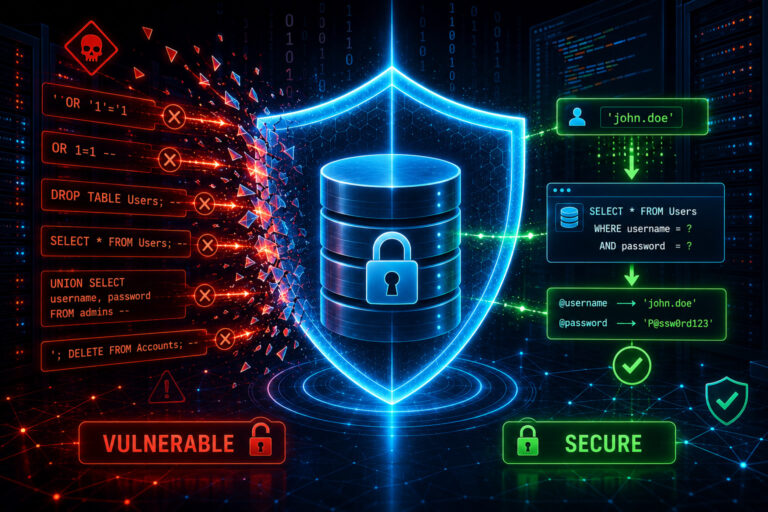
Understanding the benefits parameterized queries security performance is critical for building resilient, high-throughput enterprise web systems. At Secure Coding Practices, software engineers emphasize that parameter binding provides an unbreakable defense against SQL injection by isolating executable commands from variable data.…
  • Leon I. Hicks
  • October 19, 2026
  • Input Validation & Sanitization

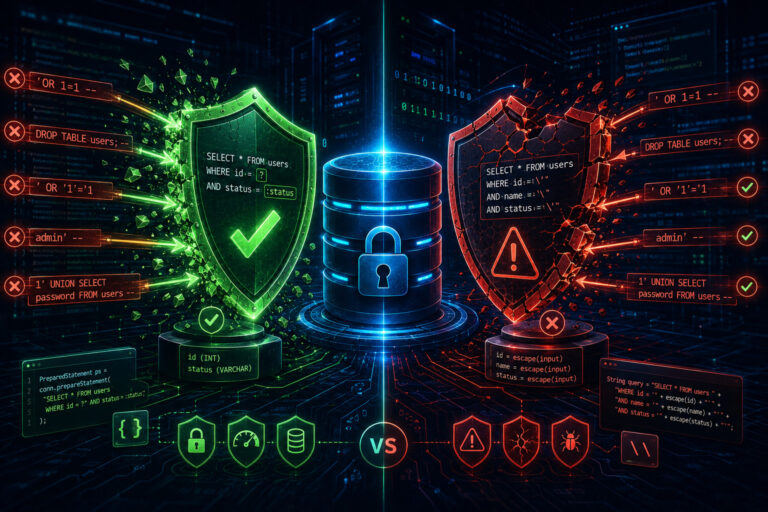
Parameterized Queries Vs Escaping Input for Database Security

Parameterized Queries Vs Escaping Input for Database Security

Evaluating parameterized queries vs. escaping input helps developers choose safer ways to prevent SQL injection. Parameterized queries separate SQL commands from user-supplied values, so input is treated as data rather than executable SQL. Escaping input attempts to neutralize special characters,…

  • Leon I. Hicks
  • October 18, 2026
  • Input Validation & Sanitization

Using Prepared Statements Java Php for Secure Database Queries

Using Prepared Statements Java Php for Secure Database Queries

Prepared statements help prevent SQL injection by separating SQL commands from user-supplied values. In both Java and PHP, they allow database engines to handle input as data rather than executable SQL, reducing the risk of malicious queries. This approach also…

  • Leon I. Hicks
  • October 17, 2026
  • Input Validation & Sanitization

How Parameterized Queries Prevent Sql Injection Guide

How Parameterized Queries Prevent Sql Injection Guide

Parameterized queries help prevent SQL injection by separating SQL commands from user-supplied values. Instead of treating input as executable code, the database handles it as data, reducing the risk of attackers manipulating queries. Developers can apply this approach across different…

  • Leon I. Hicks
  • October 16, 2026
  • Input Validation & Sanitization

Mastering Parameterized Queries for DB Security

Mastering Parameterized Queries for DB Security

Securing backend data infrastructure starts with controlling how your application communicates with its database. Adopting parameterized queries for DB security enforces a strict boundary between executable SQL logic and external input, eliminating the structural ambiguity that makes SQL injection possible.…

  • Leon I. Hicks
  • October 15, 2026
  • impact improper canonicalization handling, Understanding Input Canonicalization

Impact of Improper Canonicalization Handling

Canonicalization flaws can cause security checks to approve one form of input while another component interprets it as a different resource, route, or command. MITRE CWE-180 describes this as a validation-order problem: the application checks data before it has been…

  • Leon I. Hicks
  • October 14, 2026
  • Input Validation & Sanitization, Libraries handling canonicalization securely, Understanding Input Canonicalization

How Libraries Handle Canonicalization Securely

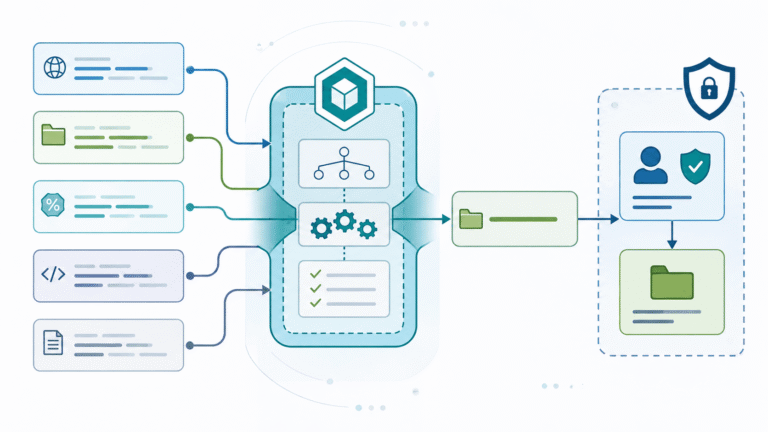
Data flow diagram showing libraries handling canonicalization securely before granting file access.

Canonicalization should turn equivalent input into one clear form before authorization, but it can’t replace the final security check. The application still needs to enforce access rules when it performs the requested resource operation. Path handling is a common source…

  • Leon I. Hicks
  • October 13, 2026
  • Testing for canonicalization vulnerabilities methods, Input Validation & Sanitization, Understanding Input Canonicalization

Testing for Canonicalization Vulnerabilities: Methods

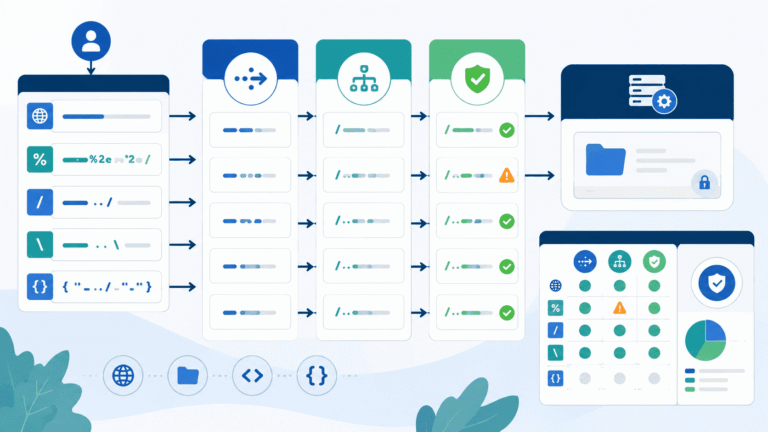
testing for canonicalization vulnerabilities methods with input equivalence and validation checks.

Canonicalization testing checks whether each layer reads the same input in the same way. That matters because security checks can fail when one layer decodes, normalizes, or rewrites data before another layer uses it. MITRE CWE-180 points to validation before…

  • Leon I. Hicks
  • October 12, 2026
  • validating input after canonicalization important, Input Validation & Sanitization, Understanding Input Canonicalization

Validating Input After Canonicalization Matters

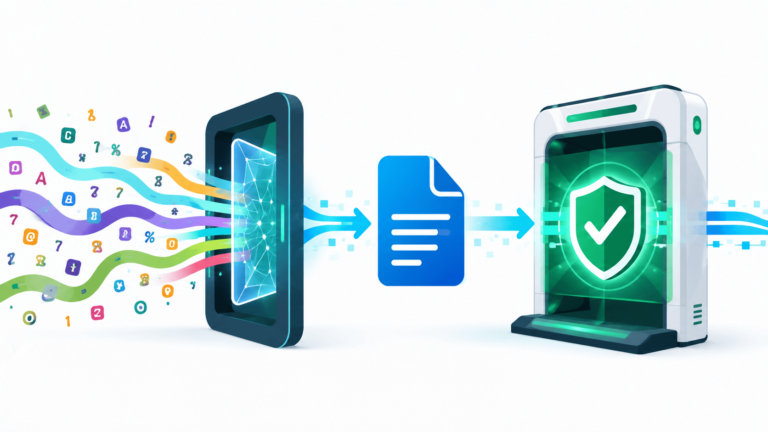
Phone data streaming into a document then a secure server, showing why validating input after canonicalization important.

Validate input after canonicalization, not before. Security checks should inspect the same form of data the application will use. MITRE lists this ordering issue as CWE-180, which covers validation before canonicalization and can contribute to problems such as path traversal.…

  • Leon I. Hicks
  • October 11, 2026
  • Understanding Input Canonicalization, Input Validation & Sanitization, normalizing user input securely best practices

Normalizing User Input Securely: Best Practices

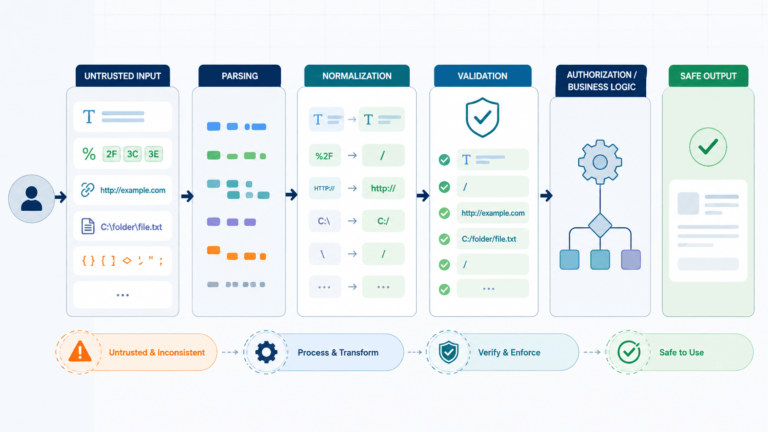
Diagram illustrating normalizing user input securely best practices from untrusted input to safe output.

Secure Coding Practices explains why secure input normalization should happen before validation and security checks. Untrusted data needs a consistent internal form first. If validation runs too early, later decoding or canonicalization may reveal content that bypassed those checks. So…

  • Leon I. Hicks
  • October 10, 2026
Prev
1 2 3 4 5 6 7 … 60
Next
Secure Coding Practices

Join a thriving global community of developers dedicated to writing cleaner, safer, and more resilient code. Whether you're just starting out or leveling up your skills, this bootcamp gives you the practical knowledge and hands-on experience needed to identify vulnerabilities, apply secure coding principles, and build software that stands up to real-world threats.

Join the Next Bootcamp →

  • About us
  • Blog
  • Bootcamp
  • Disclaimer
  • Contact us
  • Privacy Policy
  • Terms & Conditions

Copyright © 2026 SecureCodingPractices.com — All rights reserved.