Skip to content
No results
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Software Composition Analysis (SCA)

Benefits Using SCA Development Lifecycle for Teams

Team illustration of benefits using SCA development lifecycle across plan, code, scan, build and monitor stages

The benefits using SCA development lifecycle are straightforward. Your modern software is assembled, not built from scratch. Modern software often relies heavily on open-source and third-party dependencies. This reality makes SCA a foundational practice for building resilient applications, not just…

  • Leon I. Hicks
  • August 13, 2026
  • Software Composition Analysis (SCA)

How SCA Tools Work Process in Modern Development

Diagram showing how SCA tools work process to scan, analyze and flag risky open-source dependencies

How SCA tools work process begins with identifying the open-source parts used in your software. A Software Composition Analysis (SCA) tool shows you what those parts are. It creates a list called an SBOM, checks for security flaws and licensing…

  • Leon I. Hicks
  • August 12, 2026
  • Common Vulnerabilities & Attacks, Software Composition Analysis (SCA)

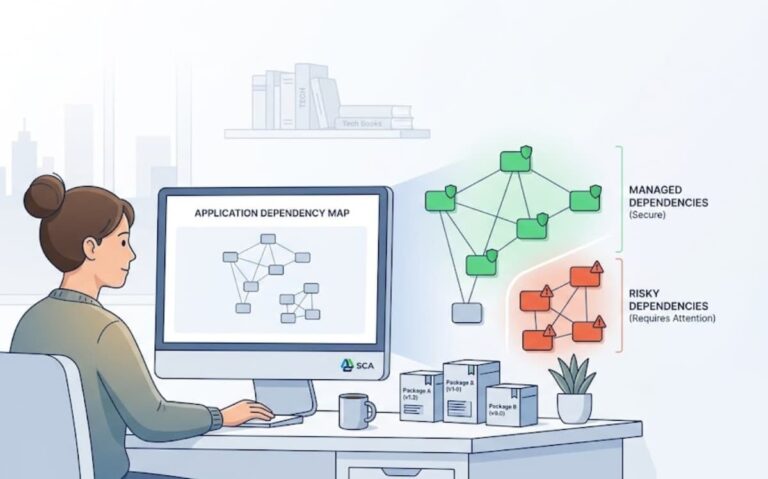
Importance SCA Dependency Management: What Teams Need

Analyst reviewing application dependency map showing the importance SCA dependency management brings to security. 

SCA dependency management helps teams track and control the open source components used in their applications. It identifies vulnerable libraries, outdated packages, and possible license issues before they create bigger problems.  As software projects grow, manually checking every dependency becomes…

  • Leon I. Hicks
  • August 11, 2026
  • Software Composition Analysis (SCA)

What Is Software Composition Analysis: Why SCA Matters 

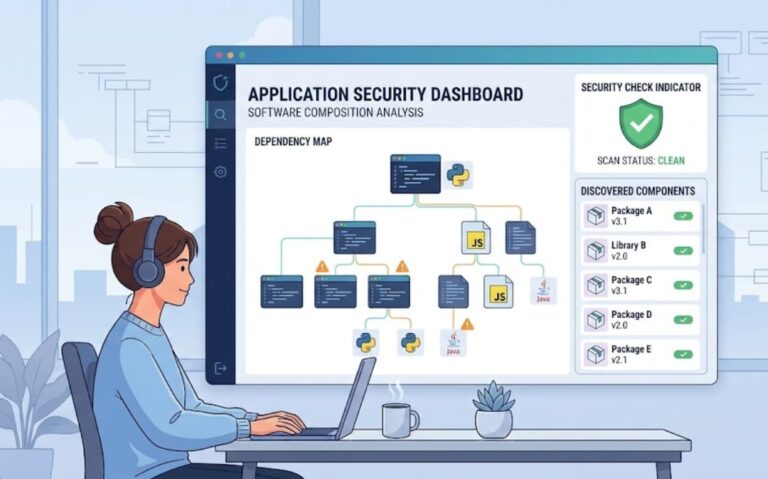
Security dashboard illustrating what is software composition analysis through a dependency map and scan status.

Software Composition Analysis (SCA) helps teams find and manage open source components, third party libraries, and dependencies used in an application. It identifies security risks, outdated packages, and license concerns before they create bigger problems. At Secure Coding Practices, we…

  • Leon I. Hicks
  • August 10, 2026
  • Common Vulnerabilities & Attacks

Software Composition Analysis (SCA): Worth Using? 

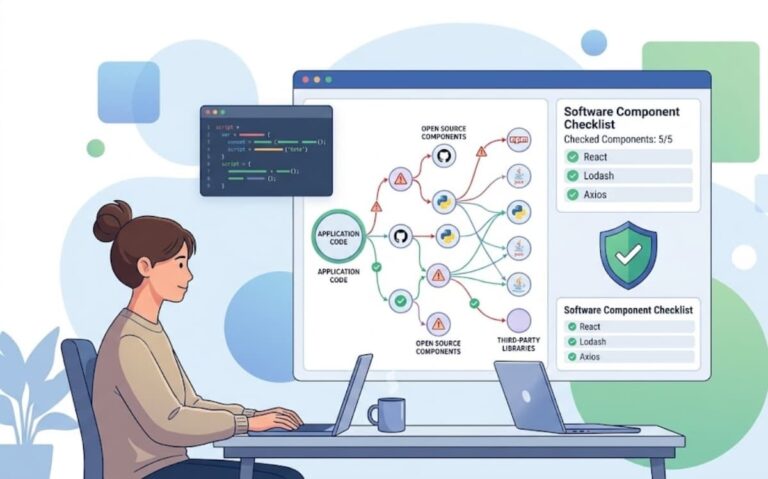
Developer reviewing application code and component checklist as part of Software Composition Analysis (SCA) workflow. 

Software Composition Analysis should be part of every modern development process because it helps teams find vulnerable dependencies early, reduce compliance risks, and improve software supply chain security before problems reach production.  Secure Coding Practices recommends making dependency scanning a…

  • Leon I. Hicks
  • August 9, 2026
  • Dangers of Insecure Deserialization, Common Vulnerabilities & Attacks

Alternative Data Formats Serialization: Worth Switching? 

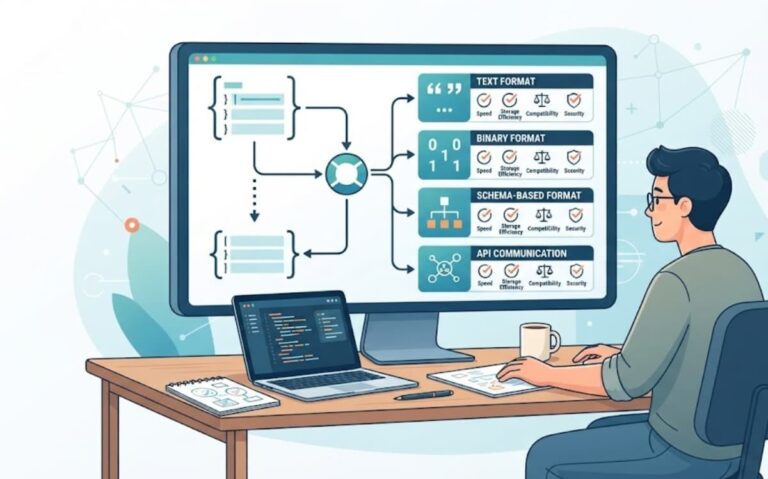
Illustrator showing text, binary, schema based, and API options for alternative data formats serialization methods.

Secure Coding Practices recommends choosing the serialization format that fits your system instead of relying on JSON or XML by default. While both are still common, they aren’t always the right choice for modern applications. Performance, compatibility, and long-term maintenance…

  • Leon I. Hicks
  • August 8, 2026
  • Common Vulnerabilities & Attacks, Dangers of Insecure Deserialization

OWASP Deserialization Prevention Tips for Secure Apps

OWASP deserialization prevention tips

Insecure deserialization remains one of the most critical threats in modern web application security. Developers often treat serialized objects as safe, inadvertently creating entry points for attackers. At Secure Coding Practices, we emphasize that applying professional security guidelines is the…

  • Leon I. Hicks
  • August 7, 2026
  • Common Vulnerabilities & Attacks, Dangers of Insecure Deserialization

Using Integrity Checks Deserialization to Stop Data Attacks

using integrity checks deserialization

Securing modern web architectures requires a shift in how developers handle object transport. As applications become increasingly distributed, the reliance on serialized data formats has introduced critical security gaps. At Secure Coding Practices, we focus on identifying and neutralizing these…

  • Leon I. Hicks
  • August 6, 2026
  • Dangers of Insecure Deserialization

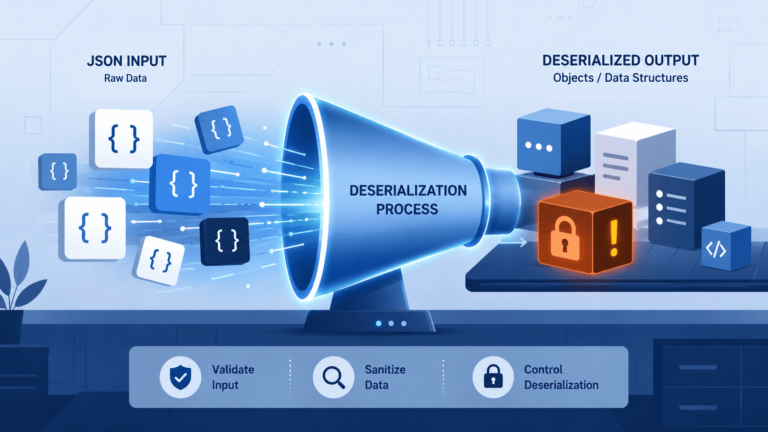
Why Data Format Deserialization Risks JSON Matter

Megaphone illustration converting raw data into objects, highlighting data format deserialization risks json processing

Data format deserialization risks JSON. The text itself is harmless. The real danger kicks in during deserialization, when your framework tries to build an object from that data. Suddenly, the parser’s behavior, library extras, and your application’s own logic become…

  • Leon I. Hicks
  • August 5, 2026
  • Dangers of Insecure Deserialization

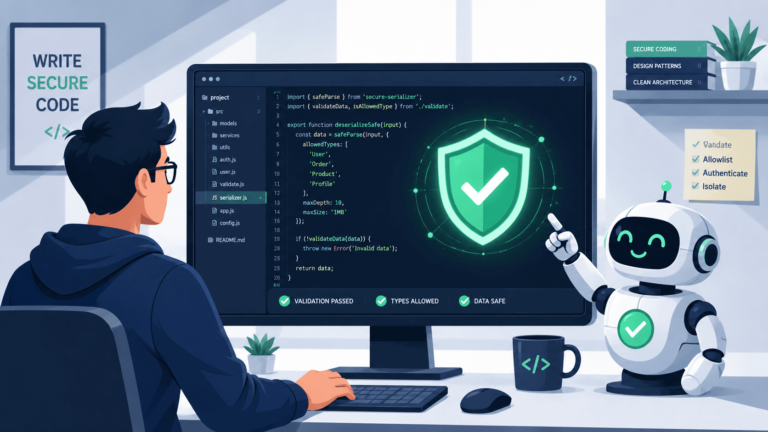
How Safe Object Serialization Practices Coding Help

Developer and robot assistant reviewing code editor, illustrating safe object serialization practices coding for security

Safe object serialization practices coding are our best defense against one of the most severe vulnerabilities a system can have. It’s about treating any serialized data as hostile until proven otherwise. This ensures the simple act of loading saved data…

  • Leon I. Hicks
  • August 4, 2026
Prev
1 … 8 9 10 11 12 13 14 … 60
Next
Secure Coding Practices

Join a thriving global community of developers dedicated to writing cleaner, safer, and more resilient code. Whether you're just starting out or leveling up your skills, this bootcamp gives you the practical knowledge and hands-on experience needed to identify vulnerabilities, apply secure coding principles, and build software that stands up to real-world threats.

Join the Next Bootcamp →

  • About us
  • Blog
  • Bootcamp
  • Disclaimer
  • Contact us
  • Privacy Policy
  • Terms & Conditions

Copyright © 2026 SecureCodingPractices.com — All rights reserved.