Skip to content
No results
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Home
  • About Us
  • Blog
  • Bootcamp
  • Contact Us
Secure Coding Practices
  • Importance of Server-Side Validation

Why Server Side Validation Crucial for Security
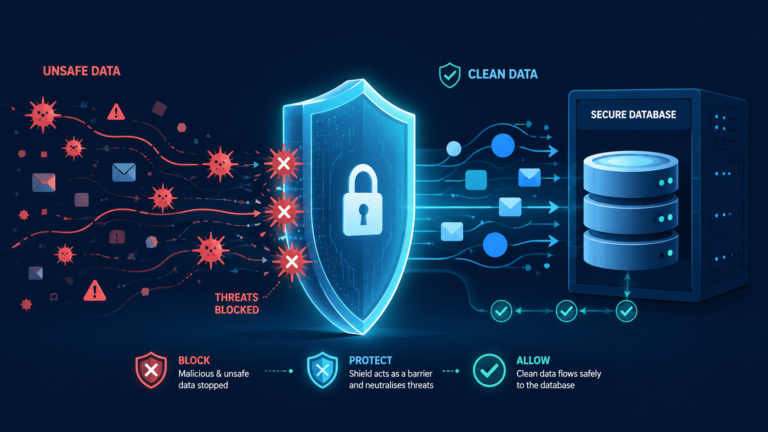
Validation gate filtering threats before a database, illustrating why server side validation crucial for data safety.

Why server side validation crucial. It’s your last defense. Think of it as the final checkpoint, the only one that truly matters. The client side is helpful, but it’s not in charge. Every bit of data coming in gets treated…
  • Leon I. Hicks
  • September 2, 2026
  • Input Validation & Sanitization

Importance of Server-Side Validation in Practice

Shield filtering safe data toward servers, illustrating the Importance of Server-Side Validation for secure systems.

Importance of Server-Side Validation. Don’t trust the browser. It’ll tell you a form is fine, that the input looks good, then send garbage to your server. The real check happens on your turf. Server-side validation is that final, unskippable gatekeeper.…

  • Leon I. Hicks
  • September 1, 2026
  • Input Validation & Sanitization

Input Validation & Sanitization Is Your First Line of Defense

Digital shield blocking malicious data, symbolizing Input Validation & Sanitization before reaching a secure database.

Input validation & sanitization is the essential guard at your code’s gate. It checks data for safety and correctness before you use it. Get this wrong, and you risk everything that follows: your database, your application logic, and your users. …

  • Leon I. Hicks
  • August 31, 2026
  • OWASP SSRF prevention measures, Common Vulnerabilities & Attacks, Server Side Request Forgery (SSRF)

A Practical Guide to OWASP SSRF Prevention Measures

Diagram showing OWASP SSRF prevention measures filtering web traffic through firewall and validation before server access

Server-Side Request Forgery (SSRF) prevention depends on using more than one control. Blocking a single attack path isn’t enough. OWASP recommends checking request destinations, limiting outbound access, confirming DNS results, and allowing connections only to trusted systems. That mix reduces…

  • Leon I. Hicks
  • August 30, 2026
  • Common Vulnerabilities & Attacks, Server Side Request Forgery (SSRF), ssrf filter bypass techniques awareness

SSRF Filter Bypass Techniques Awareness: Why Filters Fail 

Diagram showing ssrf filter bypass techniques awareness with attacker payloads bypassing web app filters to internal servers.

SSRF filter bypass awareness starts with one fact: weak validation is usually the real problem. Most failures don’t come from advanced attackers. They happen because URL checks leave gaps. OWASP continues to list server-side request forgery (SSRF) among the more…

  • Leon I. Hicks
  • August 29, 2026
  • Server Side Request Forgery (SSRF), Common Vulnerabilities & Attacks, difference ssrf csrf explained clearly

Difference Between SSRF and CSRF, Explained Clearly

Diagram showing difference ssrf csrf explained clearly through attacker requests to servers versus browsers.

SSRF and CSRF are different because they target different trust boundaries. SSRF makes a server send requests it should never make. CSRF gets a logged-in user’s browser to send requests without their approval. That difference matters more than most people…

  • Leon I. Hicks
  • August 28, 2026
  • Common Vulnerabilities & Attacks

Best Practices for Validating User Supplied URLs Securely

Python code validating user supplied urls securely with allowlists and private IP blocks

validating user supplied urls securely is a critical security practice for modern web applications that process dynamic external links, preventing server-side request forgery and malicious redirects. When engineering teams fail to implement strict boundary validation, attackers can easily manipulate input…

  • Leon I. Hicks
  • August 27, 2026
  • Common Vulnerabilities & Attacks

Best SSRF Mitigation Techniques Allowlist Strategies

Cybersecurity diagram illustrating SSRF mitigation techniques allowlist filtering safe outgoing HTTP requests while blocking malicious internal requests.

Modern web architectures frequently interface with external APIs and microservices, creating expansive attack surfaces vulnerable to server-side request forgery. When engineering teams secure their network perimeters, implementing robust ssrf mitigation techniques allowlist strategies becomes essential for preventing unauthorized internal resource…

  • Leon I. Hicks
  • August 26, 2026
  • Common Vulnerabilities & Attacks

The Impact Successful SSRF Exploitation Has on Systems

impact successful ssrf exploitation

Modern web applications frequently integrate external services and media import engines, expanding their attack surface across interconnected microservices. When security teams evaluate application risks, understanding the impact successful ssrf exploitation brings to enterprise infrastructure is critical. Server-side request forgery occurs…

  • Leon I. Hicks
  • August 25, 2026
  • Common Vulnerabilities & Attacks

Comprehensive Guide to Testing for Ssrf Potential Vectors

testing for ssrf potential vectors

Modern applications frequently handle remote resources, creating complex security challenges across interconnected architectures. Identifying server-side request forgery vulnerabilities before malicious actors discover them requires a combination of automated scanning and rigorous manual code review. When evaluating applications that handle remote…

  • Leon I. Hicks
  • August 24, 2026
Prev
1 … 6 7 8 9 10 11 12 … 60
Next
Secure Coding Practices

Join a thriving global community of developers dedicated to writing cleaner, safer, and more resilient code. Whether you're just starting out or leveling up your skills, this bootcamp gives you the practical knowledge and hands-on experience needed to identify vulnerabilities, apply secure coding principles, and build software that stands up to real-world threats.

Join the Next Bootcamp →

  • About us
  • Blog
  • Bootcamp
  • Disclaimer
  • Contact us
  • Privacy Policy
  • Terms & Conditions

Copyright © 2026 SecureCodingPractices.com — All rights reserved.